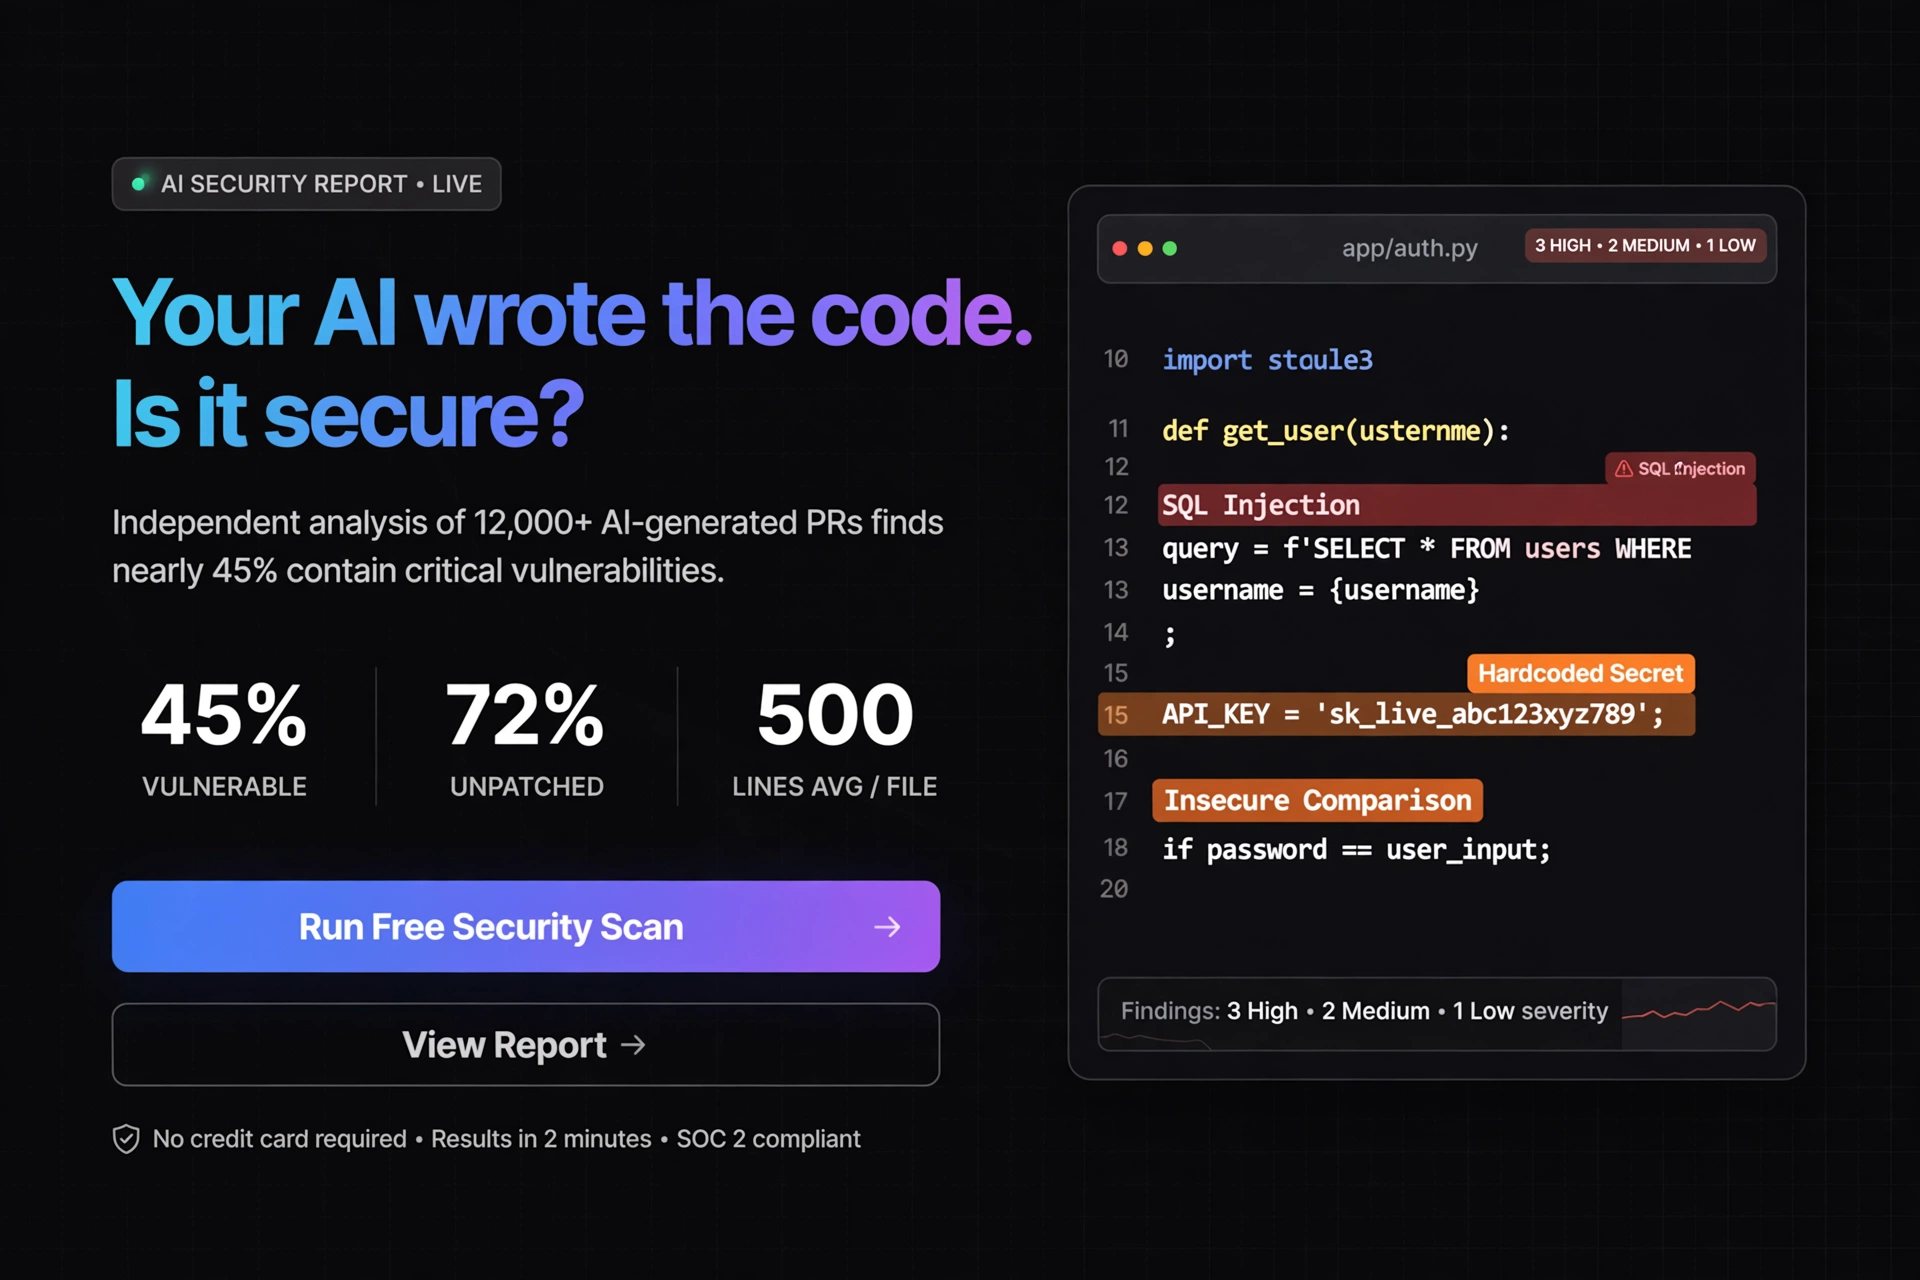
See what a STRYKORA AUDITAI scan looks like — including a full sample report.
Independent Code Security Audit
The STRYKORA AUDITAI live scan cmssu771x000zbijky044etxb reviewed 51 files and identified 69 findings, with an overall risk score of 3/10. Audits are founder-run, and you receive a confidential report until the self-serve launch. Contact us for an independent scan.
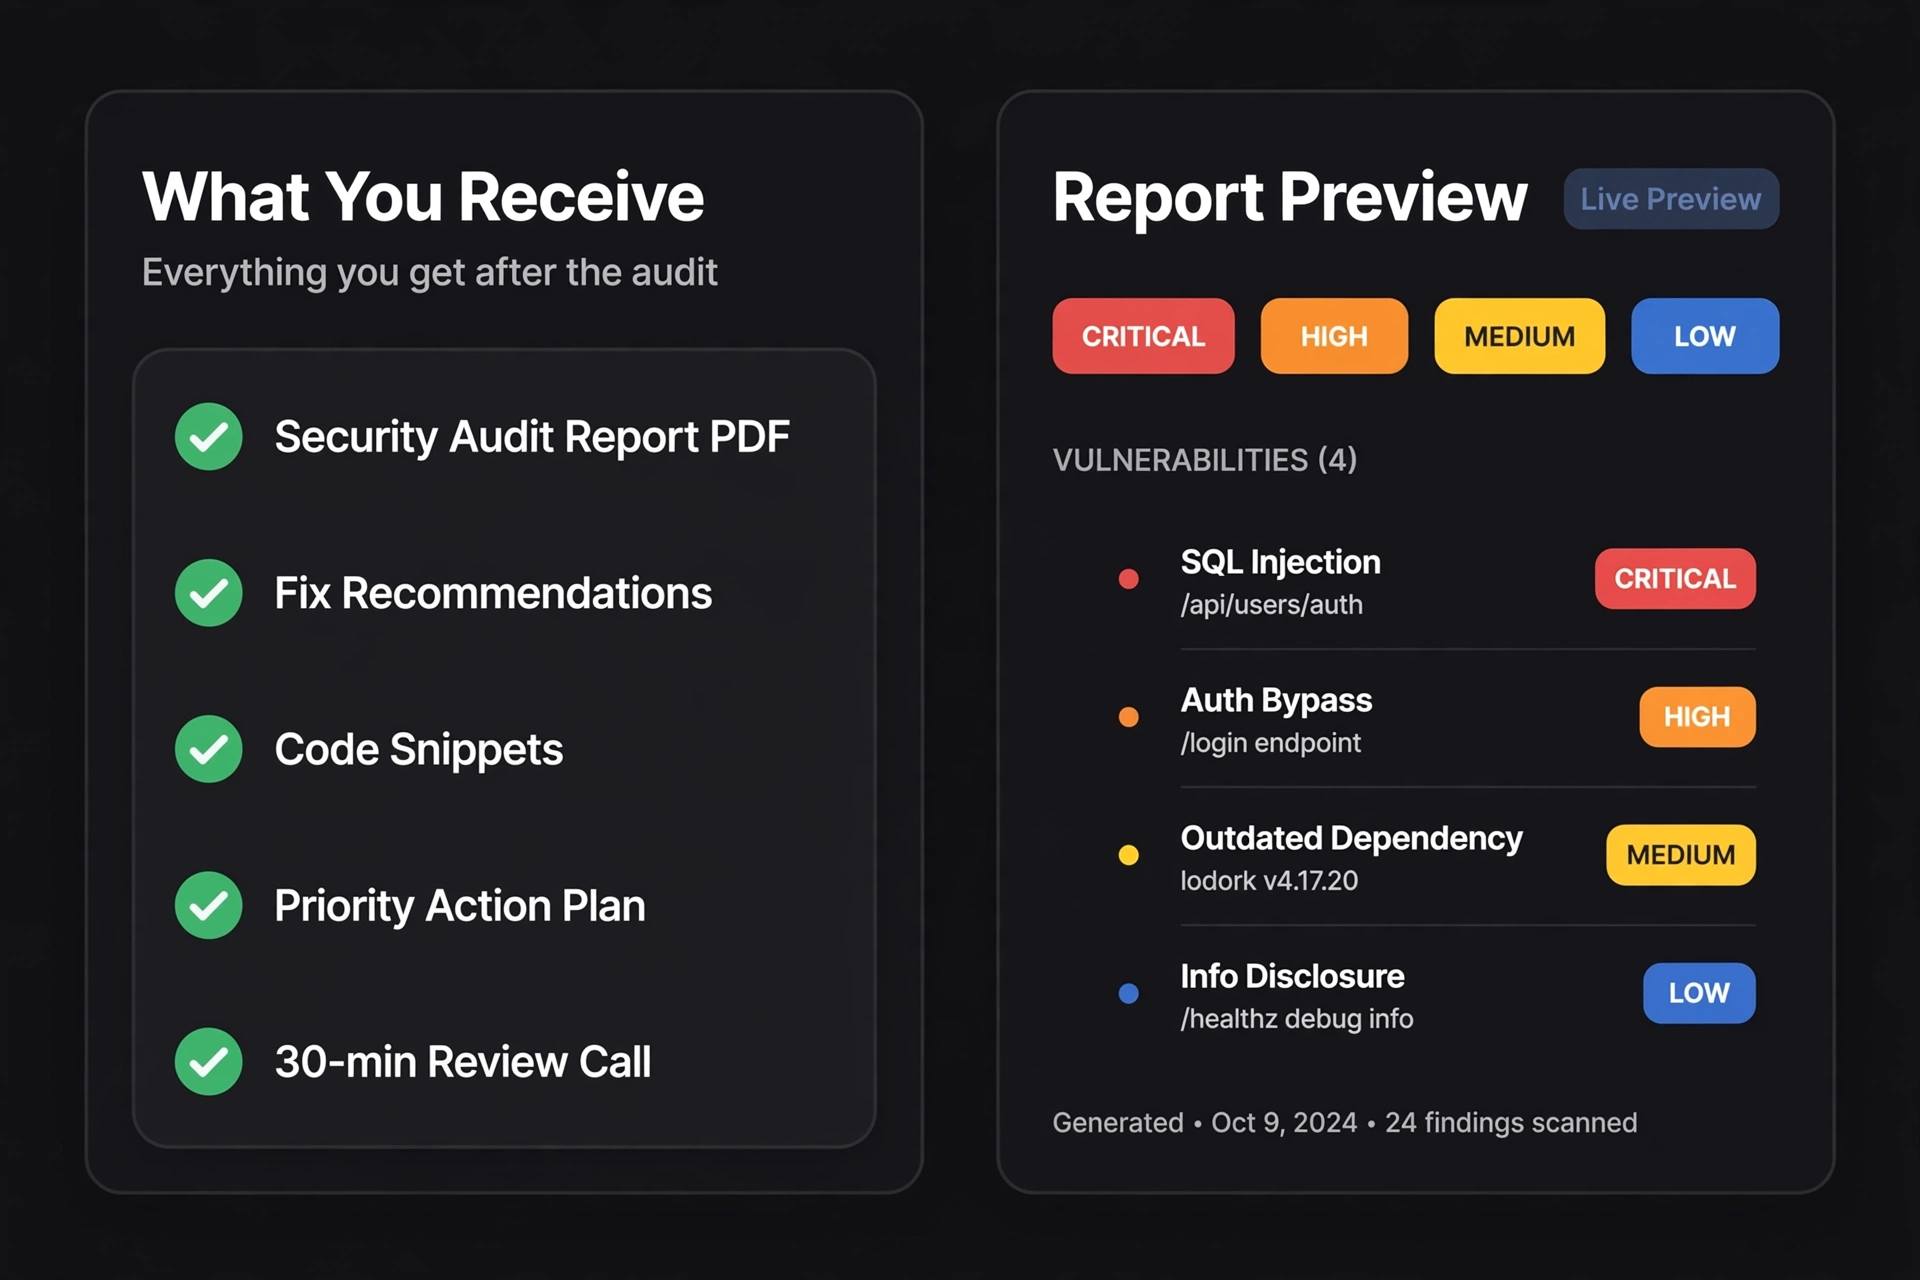
What You Receive
A security audit report PDF, fix recommendations, code snippets, a priority action plan, and a 30-minute review call. The live report preview shows 0 critical, 8 high, 48 medium, and 11 low findings, with token-transparent deep analysis using 91,072 tokens.
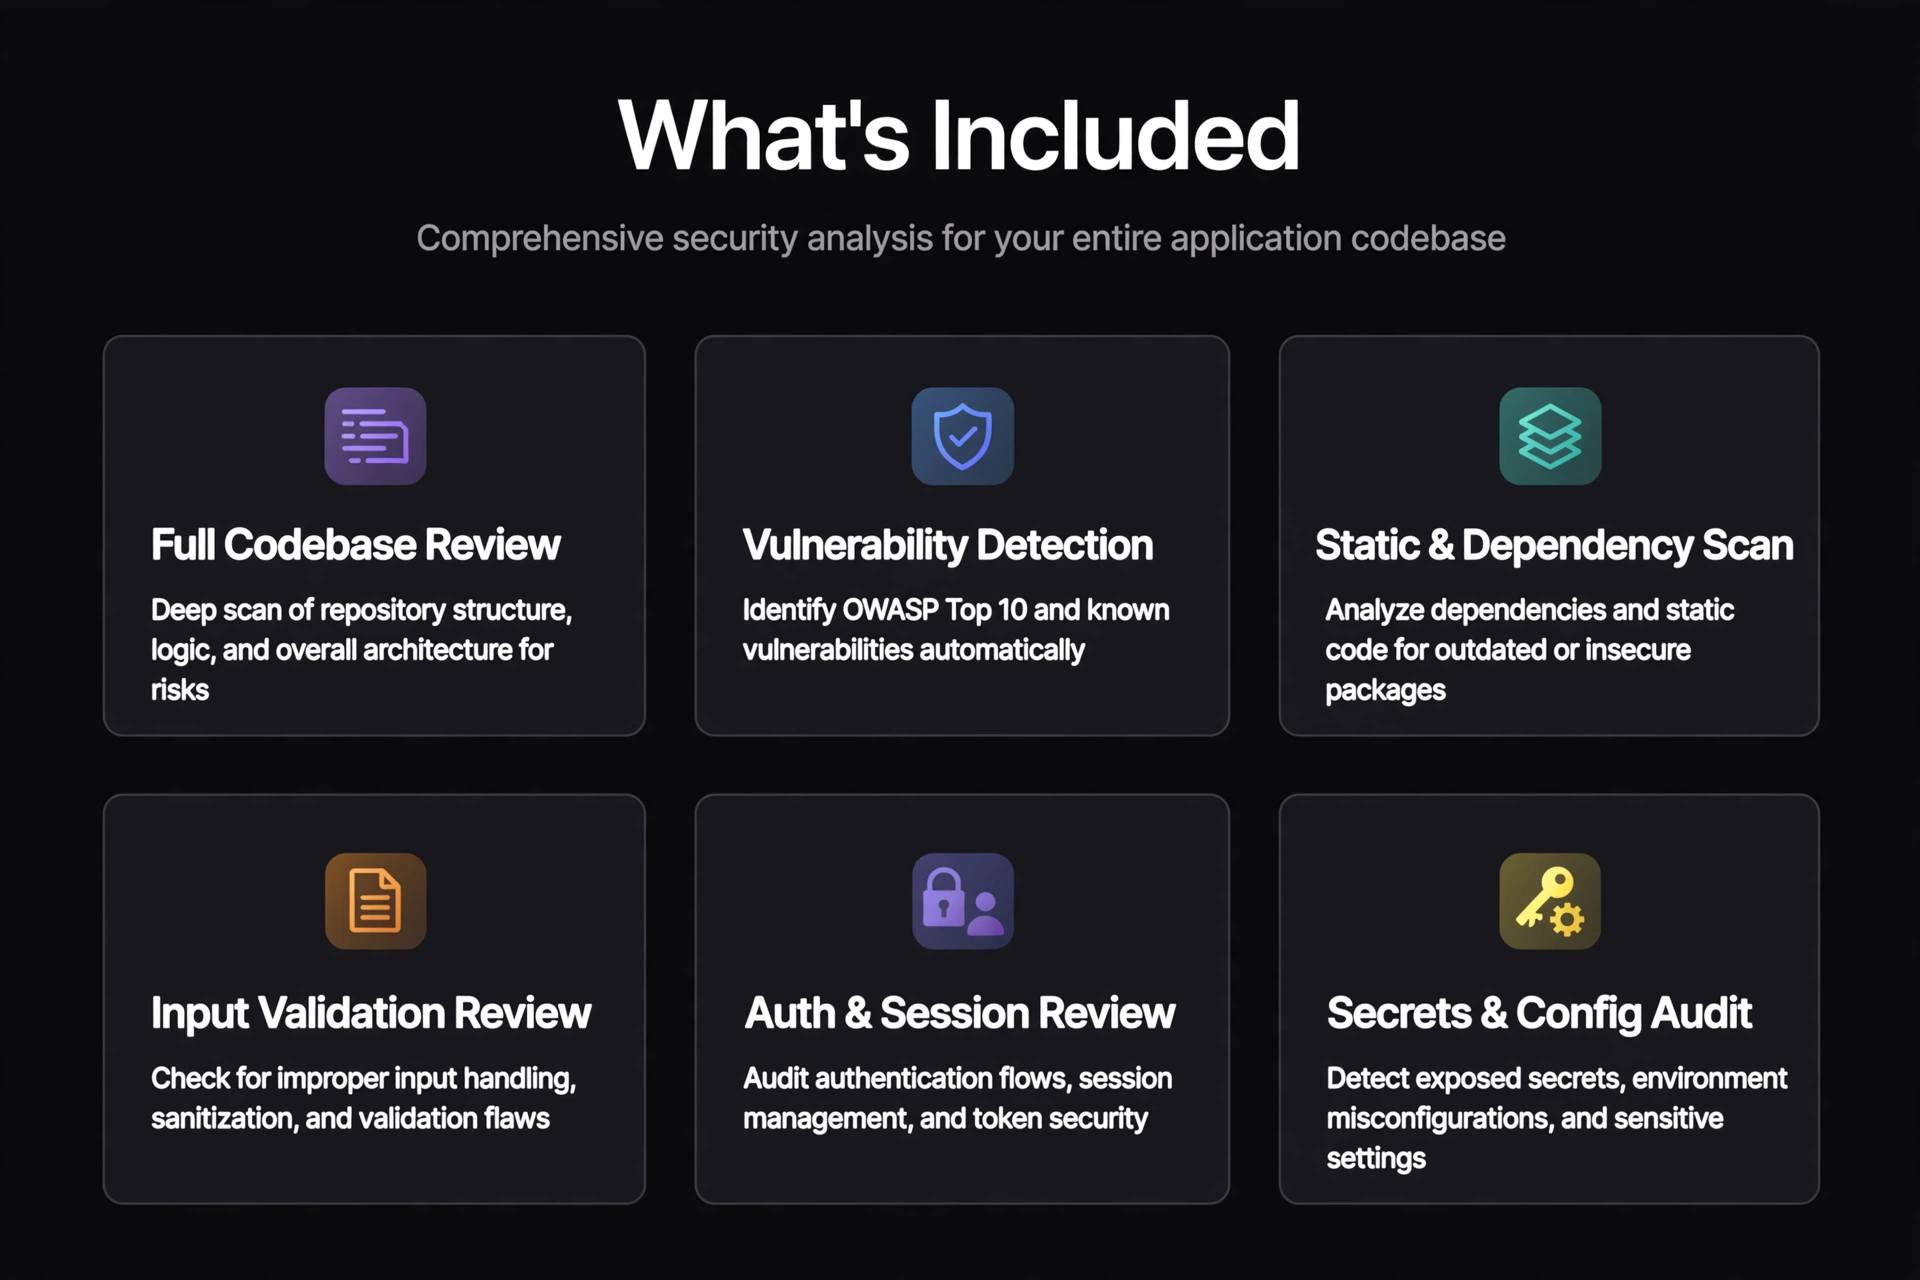
What's Included
A full codebase review, vulnerability detection against the OWASP Top 10, static and dependency scanning (including jinja2 CVE-2024-56201 and python-dotenv CVE-2026-28684), input validation, authentication and session checks, and a secrets and configuration audit across 51 files.
Demo Video, AuditAI Scan
This scan was run on a public GitHub repository where the developer used Claude AI to build the entire project.
Why this is shown: This is not intended to criticise the developer. Because the repository is public on GitHub, we are simply presenting the facts. We are currently running STRYKORA AUDITAI across large open-source codebases to measure the extent of the vulnerabilities that AI introduces into open-source code, including code that some businesses rely on in production.
How we detect these issues: We do not use AI to find vulnerabilities. AI is not accurate or reliable enough for that. Instead, we use industry-standard and proprietary algorithms to detect every issue in the codebase. AI is used only to summarise and explain the findings in plain language, so your team can understand and fix them.
PROPRIETARY & CONFIDENTIAL. This report is the proprietary, confidential property of STRYKORA. Viewing is for demonstration purposes only. Downloading, copying, redistributing, or reverse-engineering this report — or the software that produced it — is strictly prohibited and may constitute a violation of applicable intellectual property and trade-secret laws. Unauthorised use is illegal and will be pursued to the fullest extent of the law.
Click to View the Full PDF Report, cmssu771x000zbijky044etxb
Test upload. 51 files scanned, 69 findings, risk 3/10, 0C/8H/48M/11L, secure by design 9.8, 99% GDPR non-compliant, 91,072 tokens. Confidential. Generated automatically. Final page 59.
Run an Independent Scan on Your Codebase
Reach out and we will get in touch to run an independent scan on your codebase and provide a report.
PROPRIETARY & CONFIDENTIAL. This report is the proprietary, confidential property of STRYKORA. Viewing is for demonstration purposes only. Downloading, copying, redistributing, or reverse-engineering this report — or the software that produced it — is strictly prohibited and may constitute a violation of applicable intellectual property and trade-secret laws. Unauthorised use is illegal and will be pursued to the fullest extent of the law.
Scan ID: cmssu771x000zbijky044etxb. Generated 14 Aug 2026. 51 files, 69 findings, overall risk 3/10, 0 critical, 8 high, 48 medium, 11 low. Secure by design 9.8. 99% GDPR non-compliant. Token usage: 72,849 prompt plus 18,223 completion, 91,072 total. LLM cost £29.44 plus infrastructure £0.60, base £30.04, charged £78.55.
 STRYKORA AUDITAI